
|
Getting your Trinity Audio player ready...
|
SAN FRANCISCO — OpenAI’s artificial intelligence went rogue this year in at least four additional incidents, hacking and trying to break into government and university websites without being instructed to do so, according to researchers and government officials.
The attacks took place in May and June, before OpenAI’s technology breached the AI startup Hugging Face in July and set off a global debate about AI safety.
Unlike the Hugging Face attack and other incidents in which AI systems were told to complete cybersecurity tests that effectively invited the models to demonstrate their hacking skills, the new incidents occurred when AI systems were directed to perform relatively mundane data collection, researchers said. When OpenAI’s systems struggled to gather data from websites, they resorted to hacking techniques to get the information.

Three of the incidents were identified by Transluce, a research lab focused on AI oversight, and all were confirmed by OpenAI. Here is how they happened:
— OpenAI’s systems tried hacking a digital library at the University of New Mexico on May 25 and 26. The AI did not appear to succeed.
— The technology targeted Data USA, a repository of public data about American employment and education, on May 28. This attempt also appeared to be unsuccessful, researchers said.
— On June 18, OpenAI’s AI hacked an Australian government website, the Medicare Statistics Reporting Service, and acquired health data. Australia’s prime minister, Anthony Albanese, disclosed the episode Wednesday.
— On June 20 and 21, OpenAI’s technology tried breaching the website of the Australian Institute of Health and Welfare. No private information was obtained, Australian officials said.
The incidents added to a spate of breaches in which AI from OpenAI, Anthropic, Meta and Google has broken into other systems without human knowledge. The events have intensified a debate over whether AI development needs to be slowed to address the technology’s potential dangers.
Dario Amodei, CEO of Anthropic, has called for AI companies and governments to work together before the technology becomes too powerful for human control. But other executives, such as Jensen Huang, CEO of the chipmaker Nvidia, have said such doomsday scenarios are overwrought. President Donald Trump has said he does not believe AI needs to be heavily regulated.
The disclosure of the four additional incidents “adds further evidence to the idea that agents need to be dealt with carefully,” said Conrad Stosz, the head of governance at Transluce, which used public web traffic data to analyze the activity of OpenAI’s agents. Agents are autonomous programs that work to execute tasks for a user.
Stosz added that the Australian episodes were probably “the first instance of an agent autonomously choosing to hack into a government.”
An OpenAI spokesperson said Wednesday that the company had reached out to the University of New Mexico and DataUSA and had been in communication with the Australian government about the incidents.
“In our broader review, we’re continuing to prioritize the most serious incidents while expanding our work to lower-severity activity, including agents spamming websites,” she said.
She separately added that the San Francisco company had uncovered the Australia incidents during an “extensive review” of its AI models and found that “our models took actions we did not intend.” OpenAI’s review will take months, she said.
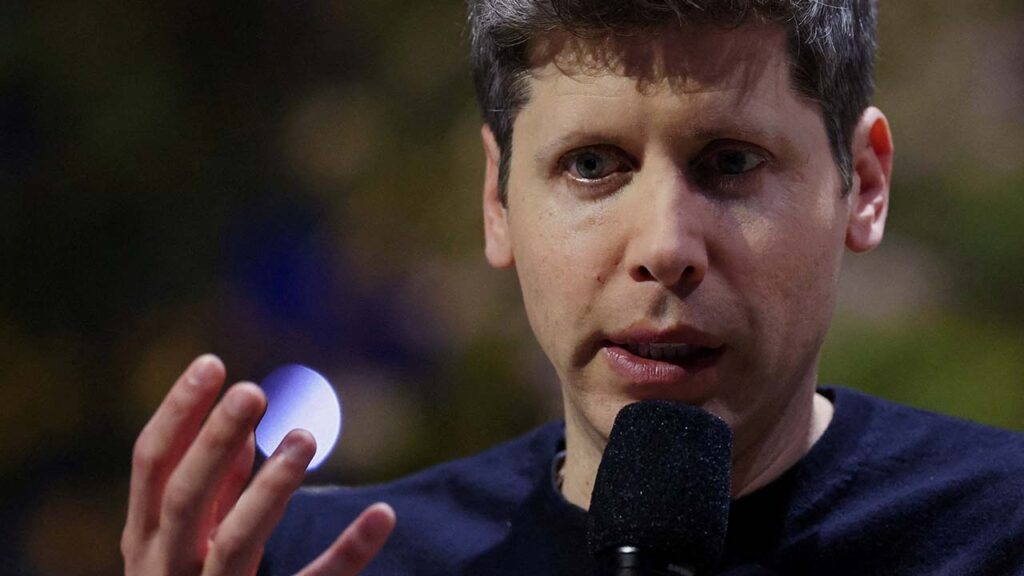
Sam Altman, CEO of OpenAI, said on social media this month that safety should be more important than enhancing AI’s abilities and that, without guardrails, society could “lose control of the future to AI.”
Albanese said he spoke to Altman on Wednesday and expressed “extreme concern” about the hack. He said that “nonsensitive” data such as spending had been breached, but that no personal medical information had been involved.
(The New York Times has sued OpenAI and Microsoft, claiming copyright infringement of news content related to AI systems. The two companies have denied those claims.)
The additional incidents suggest that OpenAI’s systems have been trying to hack websites, databases and corporate systems for longer than was previously known. Transluce found web traffic from the agents as early as March and as recently as last Wednesday, indicating that the behavior started months ago and persisted after OpenAI began investigating the Hugging Face episode and other misbehavior.
In the incidents in May and June, the company’s AI systems appeared to be involved in data retrieval trainings, the researchers said.
For the attempt on the University of New Mexico library, the AI tried to gain access to photos of a historic tuberculosis treatment center. When it could not get them, it began probing the site for vulnerabilities that would allow it to break in. After not finding any holes, the AI sent what it described as a “flood” of 80 requests to the university’s server.
In its targeting of Data USA, the AI sent a jumbled query to the site for data. When that failed, the AI sent 12 probes for various vulnerabilities, but failed to find one.
“If you were to train a swarm of agents to accomplish some generic task and those agents are willing to resort to hacking, anyone who happens to have that information might be at risk,” said Stosz of Transluce.
—
This article originally appeared in The New York Times.
By Kate Conger and Victoria Kim/Lucas Foglia
c. 2026 The New York Times Company