
|
Getting your Trinity Audio player ready...
|
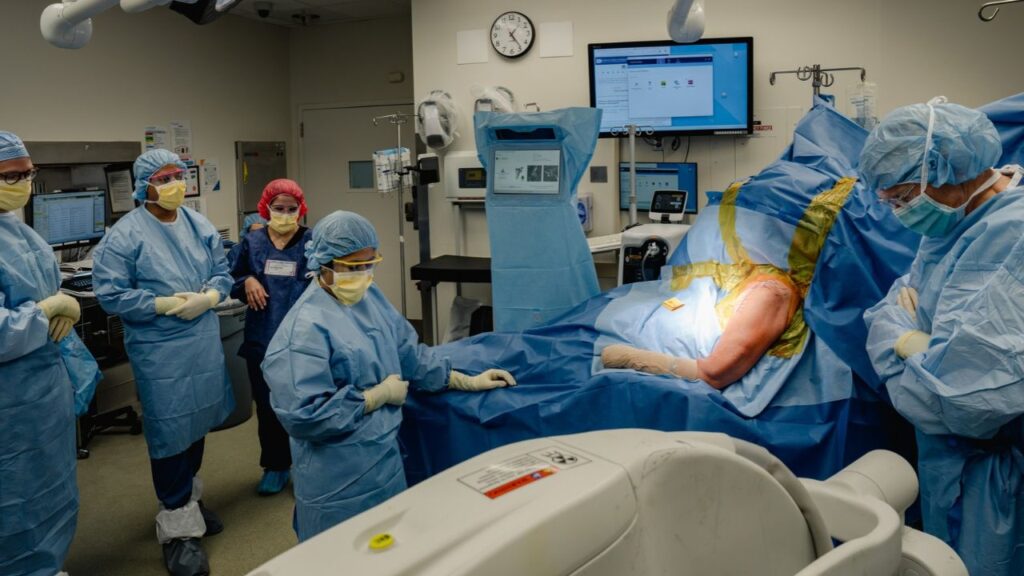
Health networks across the United States rushed to secure computer systems after the discovery of a vulnerability in ubiquitous Java software, searching for signs of intrusion and applying patches that Oracle, Java’s owner, issued as a rapid fix.
The American Hospital Association said it was not aware of any negative impacts on hospital operations, other than the disruption of racing to respond to potential threats with new defenses.
Technology departments were in a race to “patch before they hack,” said John Riggi, the association’s national cybersecurity adviser. Recent system failures including air traffic control, banking and Microsoft software programs, Riggi said, “have placed hospital cyber teams at an unprecedently high security posture.” The causes of those failures are under review.

“Hospital cybersecurity teams across the country are using sophisticated tools to actively scan their entire internal networks, medical devices and internet-facing programs, searching for instances of the identified Java vulnerability, and patching as soon as possible,” Riggi said.
The healthcare industry has been under siege for years by ransomware attacks that have paralyzed their systems while hackers demanded payments of millions of dollars.
Hospital executives rarely disclose whether they paid the ransom, but their settlements in patient class-action lawsuits provide a means of tracking the phenomenon. The healthcare industry had the highest number of federal court settlements of any sector from 2010 to 2025, with 118, according to a new analysis by Cornerstone Research.
Hospitals use Java in several ways. With its patch Tuesday, Oracle listed 21 products for which it should be used. Oracle bought Cerner, a large electronic health records vendor, in 2022.
Epic Systems, the largest health records vendor, said Tuesday that its systems were not affected. Judy Faulkner, Epic’s founder and CEO, disclosed in September that Epic’s own system analysis using artificial intelligence tools had uncovered a flaw that could allow hackers to enter health records systems and possibly change data undetected. It issued a patch.
On Tuesday, consulting and group-purchasing companies for hospitals said that thousands of clients were working around the clock to secure systems. The use of AI to examine system integrity and in hacks has dramatically accelerated the pace of cybersecurity response.
“This is the crazy world we live in,” said Florian Quarré, chief data and AI officer at Premier, a group purchaser. “This came out hours ago, and is another example of a crack in well-wielded armor that is cracked open with new tools.”
He said the incident had exposed “the complexity related to these flaws in modern systems, the velocity at which they are found and the speed at which they are exploited.”
Security specialists must assume that hackers are using AI to exploit flaws in hospital systems, the experts said.
“The key is to move with urgency, follow the evidence as the threat evolves and focus resources where they can meaningfully reduce risk,” said Juli Rhoden Cunningham, chief information security officer at Vizient, a healthcare consulting company.
Riggi of the hospital association said that hospital technology teams have been on heightened alert for weeks. Among other cases, he cited a recent hack of the blood storage unit temperature systems in France.
–
This article originally appeared in The New York Times.
By Christopher Rowland/Shuran Huang
c. 2026 The New York Times Company